 11

The recent theft of over 153 million US and Canadian driver’s licenses, a staggering breach that exposed sensitive personal information, serves as a stark warning: the safest place for a copy of your driver’s license is nowhere at all. These leaked identities, reportedly originating from an identity verification provider, surfaced on the dark web platform Nexus, joining millions of other compromised identity and travel documents. This incident underscores a growing vulnerability in how sensitive data is handled, a problem amplified by a recent cyberattack on fintech company Revolut.
Revolut disclosed that a hacker, by posing as a legitimate entity, tricked the company into surrendering extensive customer data, including copies of passports and verification selfies. The perpetrator is now systematically releasing the identification documents of 680 customers online, demanding a ransom of 10,000 Bitcoin. This situation presents a significant irony, as the very "Know Your Customer" (KYC) processes designed to enhance financial system security by verifying customer identities and preventing illicit activities, paradoxically create massive data repositories that become prime targets for criminals.
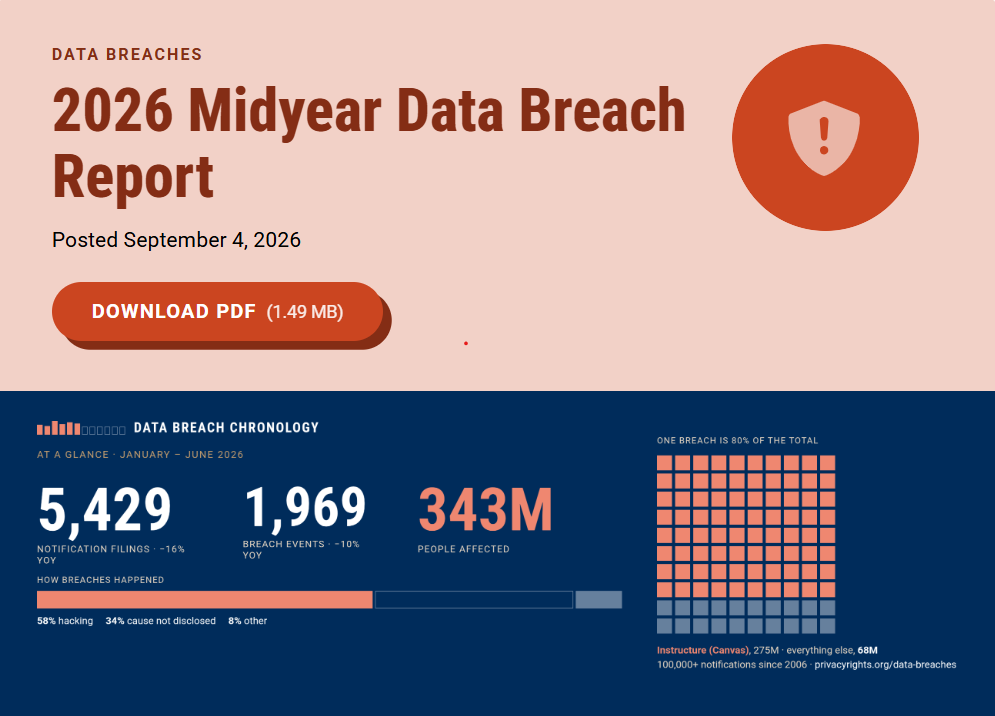
The scale of the problem is alarming. In the first half of 2026 alone, data breaches in the United States affected at least 343 million individuals, according to the Privacy Rights Clearinghouse. This pervasive data vulnerability exists despite the availability of technologies like zero-knowledge proofs, which enable identity verification without the need to store sensitive documents. Efrat Fenigson, host of the "You’re The Voice" podcast and a vocal advocate for privacy and KYC reform, expresses frustration with the current regulatory landscape. "When regulators keep mandating a model that guarantees this outcome – while the technology to verify without storing already exists – it raises a red flag," Fenigson stated. "It implies there is a lack of rational thinking and real will to solve problems." The question remains: how many more devastating data leaks will it take before a meaningful shift in approach occurs?
KYC’s Evolution: From Verification to Data Hoarding
Current KYC systems have largely evolved around the assumption that financial institutions must obtain and store copies of customer identification documents, such as passports or driver’s licenses, and retain evidence of these checks. This established model has fostered a vast ecosystem of identity providers, databases, vendors, and compliance systems, each holding separate stores of sensitive KYC data. However, each additional copy of an individual’s information represents another potential point of failure, and cybercriminals are becoming increasingly sophisticated in their methods of access.
The Revolut incident exemplifies this vulnerability. The hacker successfully exploited a loophole by sending phishing emails that mimicked legitimate Italian law enforcement communications. Lyudmyla Kozlovska, president of the Open Dialogue foundation, highlighted on social media platform X that European Union laws compelled Revolut to comply, stating, "EU AML law imposes no verification duty on the bank and provides no meaningful mechanism to check who is really behind an authenticated state request. Refusal to answer carries fines in the millions. In practice, verification is impossible."
Susie Violet Ward, director and co-founder of Bitcoin Policy UK, emphasizes that the core issue lies in the unnecessary storage of identity data. "We need to stop treating identity verification and surrendering your identity as though they are the same thing," Ward asserted. She argues that if a company’s sole requirement is to confirm a user is over 18, it should not necessitate collecting and storing additional sensitive details like a full name, address, exact date of birth, and a permanent copy of identification documents. "The irony is that KYC is designed to make systems safer, but the way we currently implement it can create an entirely different security problem," Ward added. "You can reset a password after a breach, but you cannot reset your identity in the same way."
The Solution Exists: Zero-Knowledge Proofs and Their Potential
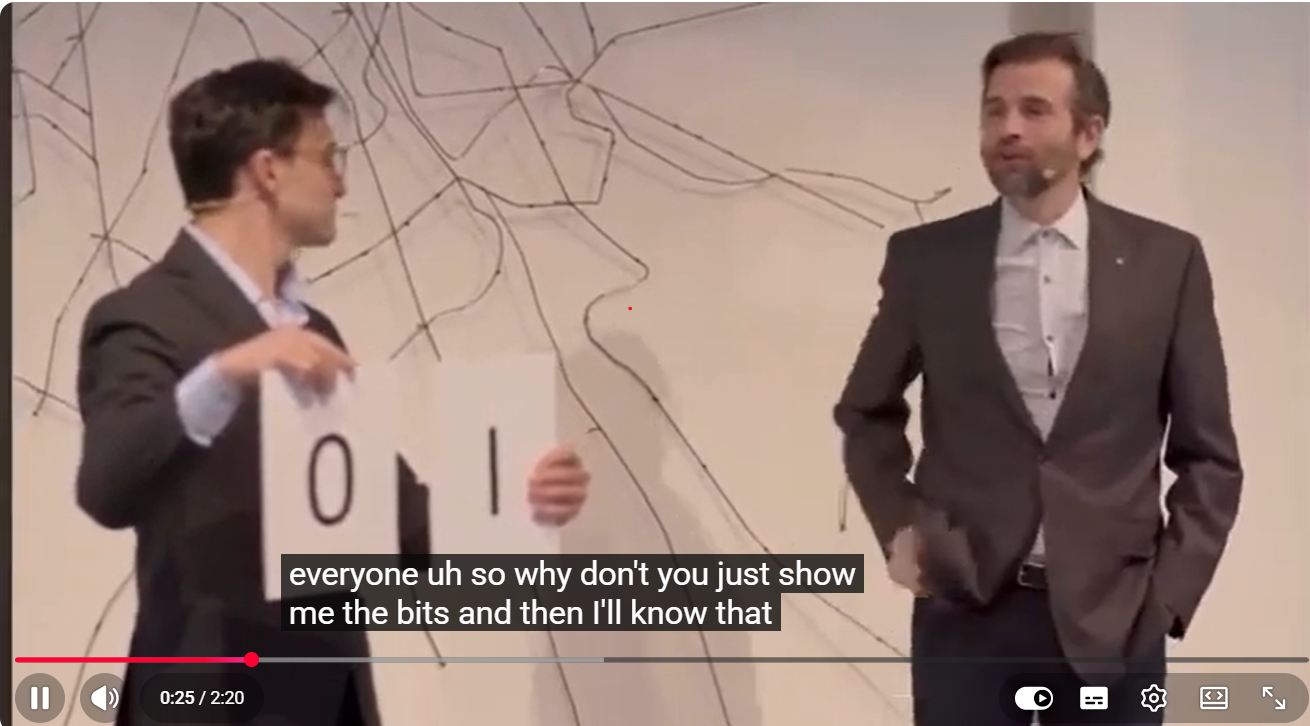
For proponents of cryptocurrency and decentralized technologies, the clear solution lies in the adoption of zero-knowledge proofs (ZKPs). ZKPs are a cryptographic method that allows one party to prove the truth of a statement to another party without revealing any information beyond the validity of the statement itself. For instance, a mobile application could utilize ZKPs to generate a proof confirming a user’s driver’s license indicates they are over 18, without transmitting their date of birth or a photograph of the license.
Zooko Wilcox, founder of Zcash, has provided accessible explanations of ZK technology in various forums, including a video detailing its mechanics. Evin McMullen, CEO and co-founder of Billions Network, a company specializing in privacy-preserving digital identity and ZK solutions, notes that the technology is not theoretical but is actively in use. "The technology works and is in production today, across thousands of applications and regulated institutions," McMullen stated. "What holds it back is that the entire compliance stack was built around collecting and storing copies of documents." McMullen posits that the impediment has never been the technology itself, but rather the established rules, incentives, and infrastructure surrounding it, describing the situation as "a governance and standards problem wearing a technology costume."
Obstacles to Widespread Adoption: Regulation and Understanding
The European Union is actively integrating ZKP technology into its digital identity and age verification systems. Their designs for privacy-preserving age verification allow users to confirm their age without divulging their full identity or exact date of birth. Furthermore, the EU’s Digital Identity Wallet supports "selective disclosure," enabling users to reveal only the information necessary for a specific transaction. Despite these advancements, the widespread deployment of such solutions for financial KYC remains limited.
According to McMullen, the primary barriers to broader adoption are "regulation and understanding." She elaborates, "The most common blocker is that compliance teams conflate ‘we saw the ID’ with ‘we must keep the ID,’ so they over-collect to be safe." Interoperability also presents a challenge, as cryptographic proofs are only effective if the relying party can verify them without needing to constantly re-authenticate with the issuer. This necessitates the establishment of shared standards, a complex undertaking.
Beyond Proofs: The Nuances of ZK and Identity Control
While zero-knowledge proofs offer a significant improvement by eliminating the need to collect and store raw identity documents, they do not inherently resolve all privacy and security concerns. Fenigson points out that the context to which a ZKP credential is tied remains critically important. "The incentives point toward control, not privacy," she observed. "Zero-knowledge proofs let someone prove a fact, like being over 18 or not on a sanctions list. What’s missing is what that proof gets bound to. Right now it’s usually bound to an account inside someone else’s database."
This highlights a crucial distinction: if a privacy-preserving proof is linked to an account within a third-party database, individuals remain dependent on a centralized intermediary. The ultimate control over the credential becomes paramount.
Ambiguity in Regulations and the Status Quo
In many jurisdictions, regulations do not explicitly mandate the permanent storage of raw identity documents. Instead, the practice has become a convention, largely due to historical precedent. The Financial Action Task Force (FATF) guidance, for example, explicitly considers how digital identity systems can be used for customer due diligence, rather than requiring institutions to solely rely on physical documents. The FATF’s recommendations operate as a risk-based framework, allowing individual countries to implement standards through their own legal and regulatory systems.
"In many regimes, the rule is that you must verify identity and retain records of that verification, not that you must keep the raw document image forever," McMullen explained. This suggests that a cryptographically verifiable attestation, accompanied by a record of the verification process, could satisfy compliance requirements without creating an enduring copy of the original ID. However, due to the "ambiguity" of this guidance, institutions often default to retaining all data to ensure compliance with auditors and examiners.
This inertia means that even if regulations technically permit alternative approaches, there is a reluctance to be the first to adopt them, fearing potential repercussions. As Ward aptly puts it, "There is an instinct in regulation that more information means more control and therefore more safety." This mindset is unlikely to change unless regulations are explicitly amended to accommodate and encourage the use of zero-knowledge proofs. While no system is entirely foolproof, ZKP technology significantly mitigates the risks associated with collecting and retaining vast amounts of sensitive personal information. The principle is simple: "You cannot lose what you never held."






