 11

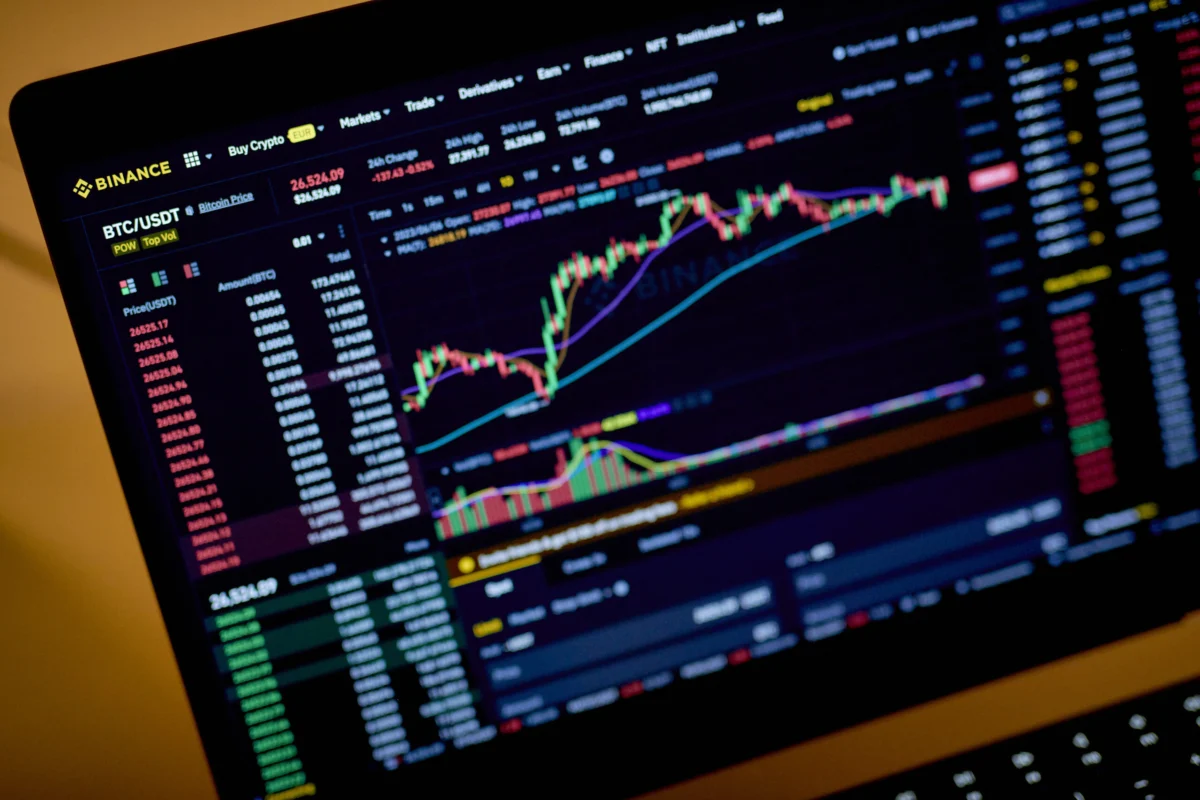
Binance, the world’s largest cryptocurrency exchange, has confirmed to TechCrunch that it is actively addressing a significant security incident, following widespread user reports detailing the unauthorized draining of funds from their crypto wallets. The unfolding situation has prompted swift action from the exchange and major stablecoin issuers, highlighting the inherent vulnerabilities within the rapidly evolving digital asset landscape.
In an emailed statement provided to TechCrunch, Binance initially acknowledged the gravity of the situation, stating it was "aware of reports of a potential security issue and are actively investigating." Crucially, the exchange sought to reassure its vast user base, asserting, "Rest assured that user funds are completely safe." This initial assurance, however, was quickly followed by more definitive actions that underscored the severity of the breach.
The statement further detailed the immediate response from Binance’s internal teams: "Our security teams are reviewing all relevant information with urgency, and we will provide updates through official Binance channels as soon as we have verified information." In a critical advisory, the exchange also cautioned users to "remain cautious of scams and should not trust unofficial links, messages, or requests for account information," a standard but vital warning during periods of heightened cyber activity and user panic.
Adding a critical layer of confirmation, Binance spokesperson Ross O’Leary subsequently clarified the exchange’s protective measures. O’Leary confirmed that Binance had "temporarily suspended withdrawals on multiple networks following a security incident as a precautionary measure." This move, while disruptive to users, is a common and often necessary step taken by exchanges during a security breach to prevent further unauthorized outflows of assets and to allow security teams to investigate and contain the threat. The suspension of withdrawals, despite the earlier assurance that funds were "completely safe," implicitly signaled that the incident was serious enough to warrant such an extreme protective measure.
News of the breach began circulating hours earlier when Changpeng Zhao, the influential founder of Binance, took to X (formerly Twitter) to address the unfolding crisis. Although Zhao no longer holds the CEO position, he remains the company’s largest shareholder and a prominent voice in the crypto community. In his post, Zhao stated that the company had "likely been hacked," providing an early, high-profile acknowledgement of the incident. Significantly, he also expressed confidence that users’ funds would be "fully covered," an assurance that suggests Binance possesses substantial reserves or insurance mechanisms designed to protect against such catastrophic losses. However, Zhao’s post did not offer any immediate explanation for this claim or details on how the coverage would be facilitated.
The financial fallout and coordinated industry response began almost immediately, underscoring the interconnectedness of the crypto ecosystem. Financial technology giant Circle, the issuer of the USDC stablecoin, reported freezing approximately $800 million in Tether (USDT) as these funds attempted to transit through its networks. This action demonstrates the centralized control stablecoin issuers maintain over their assets, allowing them to blacklist suspicious addresses and prevent the movement of potentially stolen funds. In an even more significant move, crypto giant Tether itself, the issuer of the world’s largest stablecoin USDT, announced it had frozen an estimated $1.56 billion directly related to Binance’s hack. These combined freezes, totaling over $2.3 billion, represent a substantial portion of the suspected stolen funds and indicate a rapid, large-scale effort by stablecoin providers to mitigate the damage and hinder the hackers’ ability to liquidate their illicit gains.
The sheer scale of the theft, if confirmed, positions this event as one of the most substantial cryptocurrency breaches in history. Crypto watchers and blockchain analytics firms have been actively monitoring the movement of funds. According to independent researchers like molly.wiki, at least $2 billion has been drained from Binance’s hot wallets. Hot wallets are cryptocurrency wallets connected to the internet, used for active trading and maintaining liquidity, making them inherently more susceptible to online attacks compared to ‘cold storage’ wallets, which are offline. Some more expansive estimates, reported by CoinDesk, suggest that Binance may have lost upwards of $5.7 billion in various cryptocurrencies. It is important to note that these figures remain unconfirmed by Binance, and there is a possibility that the theft could still be ongoing as investigations continue. The discrepancy in estimates often arises from the complex nature of tracing funds across various blockchain networks and the difficulty in distinguishing genuine transactions from illicit ones during an active breach.
As of the current reporting, critical questions surrounding the incident remain unanswered. It is unclear who the perpetrators behind this sophisticated hack are, whether they are a lone actor, an organized cybercriminal group, or a nation-state entity. Furthermore, Binance has not disclosed whether it has received any direct correspondence or ransom demands from the hackers, which could provide clues about their identity or motives. The absence of such information adds to the uncertainty and complexity of the ongoing investigation.
Should the confirmed losses indeed reach into the billions, this incident would undoubtedly rank among the largest crypto breaches ever recorded, according to leaderboards that meticulously track cryptocurrency thefts, such as those maintained by rekt.news. This event would surpass previous high-profile hacks, drawing comparisons to other major incidents that have shaken the crypto world. For instance, in 2025, hackers stole a record $1.4 billion in crypto in a single breach from the exchange Bybit, an attack that was subsequently blamed on North Korean state-sponsored hacking groups known for their sophisticated cyber warfare capabilities and their use of crypto theft to fund illicit state programs. The potential scale of the Binance hack underscores the persistent and evolving security challenges faced by even the most robust platforms in the cryptocurrency industry.
Adding to a challenging day for the broader crypto market, a seemingly separate security incident occurred earlier on the same Thursday. Prediction market giant Polymarket briefly halted trading after confirming that a third-party company it utilized had been compromised. This compromise directly led to Polymarket temporarily pausing withdrawals as a precautionary measure. According to security researchers, hackers exploited this vulnerability by injecting wallet-draining code into a piece of software developed by a company called DebugBear, which was integrated into Polymarket’s system. This sophisticated supply chain attack resulted in the theft of approximately $2 million in user funds. While significantly smaller in scale than the Binance incident, the Polymarket breach highlights a different, yet equally dangerous, vector of attack where vulnerabilities in third-party service providers can cascade to compromise larger platforms and user assets, contributing to a sense of widespread security concerns across the decentralized finance (DeFi) space.