 11
 1
 2
 3
Major cryptocurrency exchanges Binance and Deribit have taken precautionary measures by revoking API keys linked to the crypto derivatives trading platform SignalPlus following a confirmed security breach. The exchanges emphasized that their own internal systems remain unaffected by the incident. However, Deribit issued a warning to its customers, stating that trading, monitoring, and automated functions through SignalPlus have ceased to operate.
In the wake of the breach, Binance co-founder Yi He issued a public advisory, urging all third-party platforms integrated with the exchange to rigorously review their security protocols and remain vigilant for any suspicious activity. He underscored that the threat landscape is dynamic and extends beyond any single entity, highlighting the interconnected nature of the digital asset ecosystem.
SignalPlus specializes in providing trading infrastructure for cryptocurrency derivatives, with a particular focus on options. The platform aims to streamline operations for professional and institutional traders by enabling them to manage their positions across multiple exchanges from a unified interface.
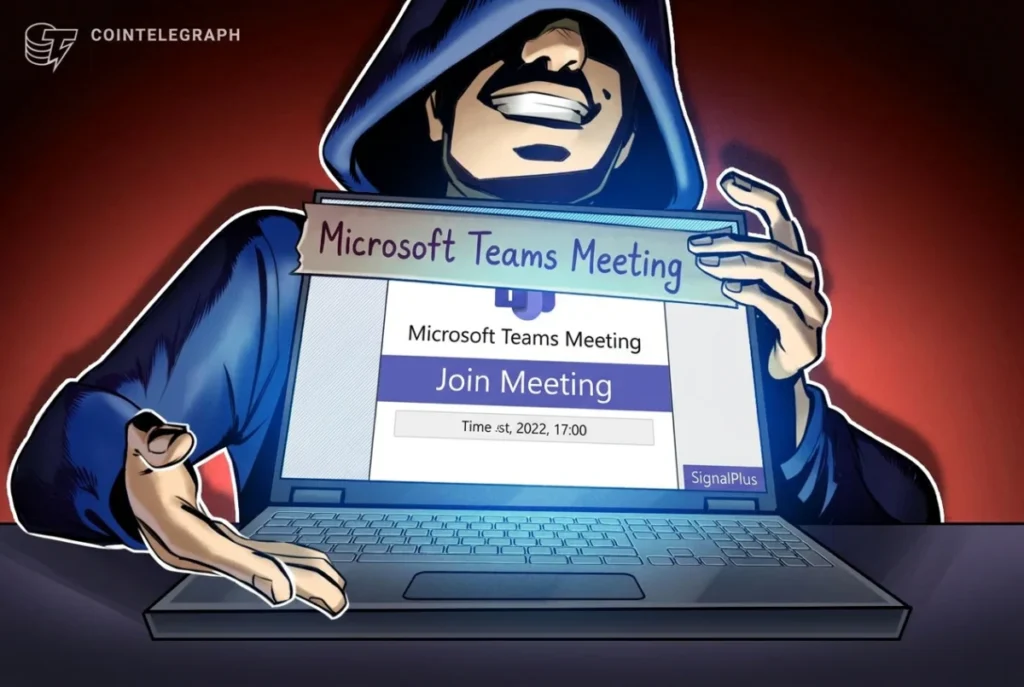
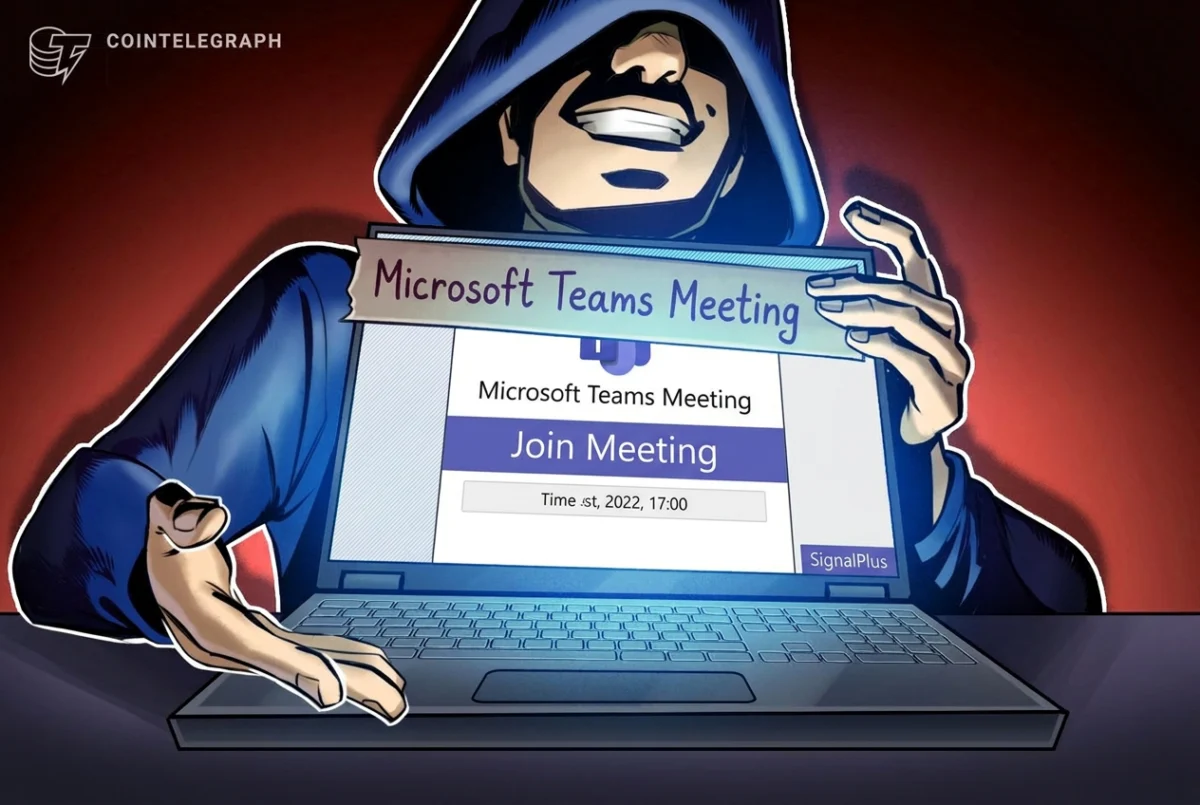
According to a statement released by SignalPlus on the social media platform X, the security incident originated from a compromised Telegram account belonging to an individual associated with a third-party technology vendor. The attacker exploited this compromised account to impersonate the contact and subsequently sent a deceptive Microsoft Teams meeting invitation to a SignalPlus engineer. This malicious invitation led to the compromise of the engineer’s computer.
The attacker reportedly remained inactive on the compromised computer for a period before leveraging the engineer’s access privileges to infiltrate SignalPlus’s internal network in the early hours of Wednesday. The company has confirmed that it has since detected and contained the intrusion. SignalPlus reported total losses amounting to less than $82,000 and has initiated the process of fully reimbursing all affected users. The platform has temporarily suspended its services and anticipates restoring full operations within the next few days, following the completion of comprehensive security reviews and the implementation of necessary software patches.
SignalPlus also acknowledged a critical oversight in its security architecture: the absence of IP whitelisting for exchange API access. The company took responsibility for this deficiency, stating, "We take responsibility for this oversight." It further committed to enhancing API access requirements and strengthening internal security controls. IP whitelisting is a security measure that restricts API access to a predefined list of authorized internet protocol (IP) addresses, thereby limiting the potential attack surface.
This incident at SignalPlus occurs in close proximity to another significant security event involving Binance. Just days prior, Binance disclosed details of a substantial hack that occurred on October 29th, resulting in a loss of approximately $6.3 billion. This preceding attack also involved the compromise of employee computers.
A post-mortem analysis released by Binance revealed that attackers, posing as recruiters, tricked an engineer into downloading a malicious file disguised as a coding assignment. This compromised computer was subsequently used by the attackers to gain access to additional systems, ultimately leading to a breach of the exchange’s wallet infrastructure.
Binance co-founder Yi He stated on Tuesday that the exchange has been actively detecting and thwarting a significant number of cyber threats. She reported that Binance identified and prevented 57 suspected North Korea-linked cyber threats in 2026 alone. These threats encompassed a range of malicious activities, including fraudulent job interviews designed to lure employees, the distribution of malicious software packages, and concerted efforts to steal employee credentials. The ongoing sophistication and prevalence of these attacks underscore the persistent challenges faced by major players in the cryptocurrency space. The SignalPlus breach serves as a stark reminder of the vulnerabilities that can be exploited, even within platforms designed to enhance security and efficiency for traders. The emphasis on reviewing third-party integrations and strengthening internal security measures by exchanges like Binance reflects a broader industry-wide effort to adapt to an evolving threat landscape.